
Fully Agentic Test Case Management Tool
Write, Track and Manage Every Manual or Automated Tests in One Agentic Test Management Platform with TestMu AI Test Manager.

What Is a Requirements Traceability Matrix? With Examples
A requirements traceability matrix (RTM) links each requirement to its tests. Learn RTM types, an Excel template, and how to show which tests passed.
Last Updated on:
On This Page
- What Is Traceability?
- Why Projects Need Traceability
- What Is a Traceability Matrix?
- What Is an RTM?
- Why an RTM Matters
- Benefits of an RTM
- Who Needs Traceability?
- RTM Parameters
- Types of RTM
- How to Create an RTM Template
- How to Create an RTM in Excel
- Covered vs Proven Requirements
- Generate an RTM From Test Runs
- Compliance Matrix
- Risk Matrix
- RTM vs RACI Matrix
- Traceability in Agile Teams
- RTM Limitations
- RTM Best Practices
- How AI Changes Traceability
- Conclusion
Before a release, someone will ask which requirements are tested and which are not. A requirements traceability matrix answers that from one table, and one generated from test runs also shows which tests actually passed.
Each row of an RTM starts with a unique requirement ID and links it to the test cases that check it, along with their latest results and any open defects. Read forward, the matrix shows requirements that have no test yet; read backward, it shows tests that no longer trace to a requirement. Safety-critical industries such as aerospace and medical devices keep one as audit evidence, and Agile teams update it sprint by sprint as user stories change.
TL;DR
A requirements traceability matrix (RTM) is a table that links each requirement to the tests that check it, along with their results and defects. It exists because a release needs proof that every requirement was tested, and a list of test cases alone cannot show which requirements have no test or which tests never ran.
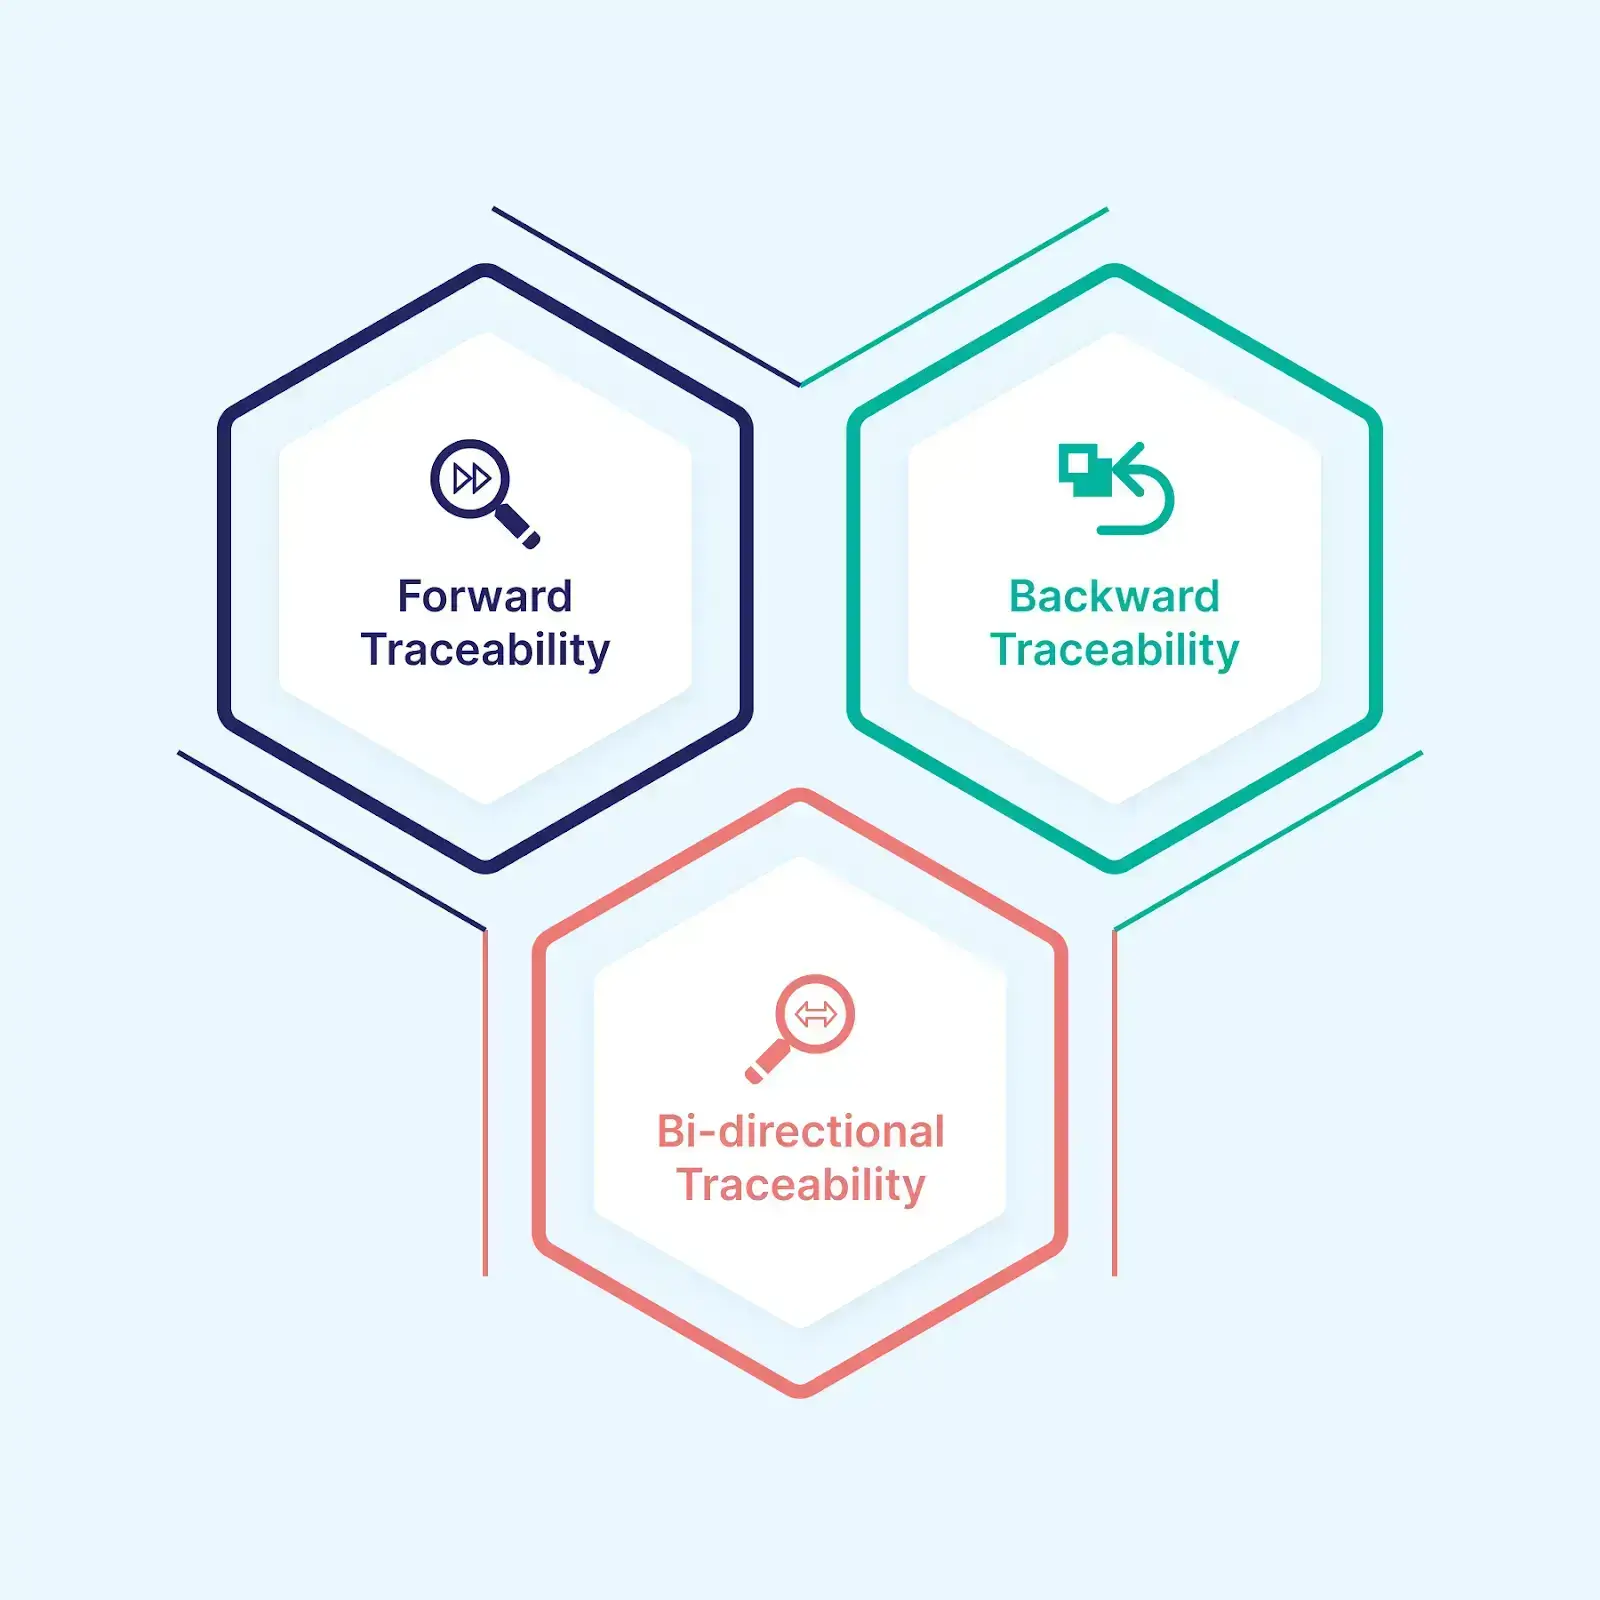
What Are the Three Types of Requirements Traceability?
- Forward traceability: Maps each requirement to its test cases, so a requirement with no test shows up as a gap before release.
- Backward traceability: Maps each test case back to a requirement, which exposes orphan tests and functionality nobody specified.
- Bi-directional traceability: Combines both directions, so a changed requirement shows which tests to rerun and every test keeps a requirement behind it.
Covered vs Proven Requirements
- Covered: At least one test is linked to the requirement, though that test may never have run or may have run against an older version of the requirement.
- Proven: A linked test passed on the current build against the current version of the requirement, with a run report or log a reviewer can open.
Can a Requirements Traceability Matrix Be Generated Automatically?
Yes. Tag each test or assertion with the ID of the requirement it checks, then build the matrix from test results in CI. Kane CLI by TestMu AI reports which acceptance criteria are proven, and TestMu AI's Test Manager tracks traceability across manual and automated runs.
Is RTM Used in Agile?
Yes. Agile teams link user stories and acceptance criteria to tests sprint by sprint, generate the matrix from test results, and review only the gaps.
What Is Traceability?
Traceability is the ability to trace each requirement forward to its design, code, and tests, and backward to its source, across the software development life cycle.
Traceability in a Software Development Life Cycle refers to understanding the dependencies and relationships between various project activities and artifacts and tracking them throughout the entire software development process.
It means establishing a link between project components such as requirements, design elements, code modules, and test cases, so team members can trace each one back to the original requirement.
Why Do Projects Need Requirement Traceability?
Projects need requirement traceability to confirm every requirement from every source is tested, improve team communication, spot issues sooner, and keep the project scope under control.
Requirements arrive from different sources, and testing teams run many tests against them. An RTM shows that each requirement was tested, which also makes it easier to transfer responsibilities and delegate work. Maintaining the matrix by hand is the usual reason to move to one of the test management tools.
A shared RTM also gives everyone the same view of progress. Several people can work in a digital matrix at once, and the links between requirements and tests show how much of the scope is done.
Traceability offers proof of meeting compliance requirements. It also shows QA teams what needs testing, because mapping test cases to requirements improves test coverage and shows how a change to a requirement affects product design.
Without an RTM:
- Testing teams cannot tell whether the test cases they wrote cover all the requirements.
- Outdated test cases create confusion during knowledge transfer, because nothing ties them to the current requirements and behaviors.
- Requirements change often in an Agile model, and nobody knows which test cases need updating. Obsolete test cases can block test execution and produce invalid defects.
What Is a Traceability Matrix?
A traceability matrix is a document that maps two baseline documents, such as requirements and test cases, to check that every item in one is covered by the other.
In the Software Development Life Cycle (SDLC), the project team uses the matrix to track each requirement and the status of its implementation. That shows the project's scope and catches work nobody asked for.
The matrix can trace requirements from their origins (such as business objectives, regulatory standards, or system requirements) through detailed requirements to their fulfillment in system components, tests, and operational systems.
It is a living document: new requirements are added as they arrive, and each one's status changes as it is fulfilled.
What Is a Requirement Traceability Matrix?
A requirement traceability matrix (RTM) is a table with one row per requirement that records the tests that check it, the latest result of those tests, and any open defects. It is the traceability matrix applied to the most common pairing in testing, requirements against test cases.
Reading across a row tells you whether a requirement is tested and whether it passed. Reading down the test column shows which tests map to no requirement. Both checks belong in software testing before each release, so no functionality ships untested.
Why Is a Requirements Traceability Matrix Important?
A requirements traceability matrix is important because it shows that every requirement has a test, so gaps, untested changes, and missed defects surface before release.
- It keeps a project on its original goals, because each requirement needs a test and a result before it counts as done.
- It points the QA team at weak areas, since a requirement with failing or missing tests is the first place to look.
- It supports design decisions, because the testing team can see which requirements a change touches before it ships.
- It shows progress in project terms, as the share of requirements tested rather than the number of tests executed.
What Are the Benefits of a Requirements Traceability Matrix?
An RTM improves change management, requirement completeness, tracking and verification, test coverage and auditability, impact analysis, risk control, requirement reuse, and team collaboration.
Traceability matters most on large projects with several teams and stakeholders, where it justifies design decisions and shows that each requirement was tested.
- Better change management - An RTM shows what a requirement change touches, so project teams can assess the effect on code, design, and testing before approving a change request.
- Completeness of requirements - An RTM ensures that no requirements remain unidentified in the requirements-gathering stage of a project. Teams involved should adequately address and implement them. It acts as a detailed checklist for verifying that the professionals involved have covered all requirements.
- Requirement tracking and verification - An RTM tracks each requirement from inception to implementation. Linking requirements to test cases, design elements, and results validates the system meets every one.
- Better test coverage, compliance, and auditability - Linking requirements to test cases ensures each is covered, exposes gaps or redundancies, and provides documented traceability records for audits by QA teams or regulators.
- Impact analysis - A Requirements Traceability Matrix enables testers to perform detailed impact analysis by identifying how requirements and other project artifacts are related. It helps assess the potential outcomes of making changes to a requirement or removing it. As a result, this allows for better and more prompt risk management and decision-making.
- Risk control - An RTM identifies risks tied to requirements and their dependencies, so you can assess how a risk affects the project and act on it.
- Reusability of requirements - Requirements Traceability Matrix helps identify reusable requirements within various modules of a project or across different projects. Once you analyze the dependencies and relationships, you can easily determine what requirements to use in future projects. This helps save a lot of time and effort at the requirements-gathering stage.
- Collaboration and communication - Business stakeholders, project managers, developers, and testers share the RTM as a common reference for requirements, progress, and changes.
Teams use the matrix throughout the Software Testing Life Cycle, from planning test coverage to tracing the root cause of a bug.
Test Intelligence from TestMu AI adds AI test insights on top of run data, which helps you spot issues before they block a release.
Who Needs Requirement Traceability?
Every industry manufacturing hardware or software can make use of requirement traceability. However, it is specifically beneficial for industries that have to prove something. For instance, industries with hefty regulations need to offer evidence of strict compliance. These are mostly safety-critical and quality-sensitive industries such as aerospace, medical, and automotive.
Aerospace must prove planes, helicopters, and other aerial vehicles are fully safety-equipped; automotive must prove the same for road vehicles. Both rely on software like door locks and data recorders working flawlessly.
That software must uphold quality standards and guard against cyber-attacks, and automotive traceability ensures safety compliance where software and hardware are closely integrated.
The medical industry needs to prove that medical devices are safe for patients to wear and use. Several agencies, such as the ISO and FDA, heavily regulate the medical device industry. Having a Traceability Matrix makes compliance maintenance easier and helps them pass audits. Traceability also helps developers analyze how change affects the quality of devices and conduct an in-depth risk analysis.
What Are the Parameters of a Requirements Traceability Matrix?
Common RTM parameters include the requirement ID, description, source, parent requirement, priority, status, design and specification, test case ID, test result, and comments.
Start with the parameters below and tailor them to the project. You can add columns for impact analysis, compliance references, and risk assessment.
- Design and specification - The design and specification parameter includes wireframe, design document, functional specification, or any artifact that comes under the design umbrella. When you link requirements to the respective design elements, it creates an alignment between what you have specified and what's implemented.
- Source - The source parameter indicates where the requirements came from. You can derive it from business documents, stakeholder interviews, regulatory standards, etc. When you know the source, you'll have a lot of context and can trace it back to the original process of gathering requirements.
- Requirement ID - You have to assign a unique identifier to every requirement. It could be a code or a number. This requirement ID facilitates straightforward referencing and eliminates confusion during discussion and documentation of specific requirements.
- Requirement description - The parameter offers a concise and clear description of all requirements. It conveys the functionality, business need, or core purpose of a particular requirement addresses. Stakeholders can easily share a common understanding through this well-written description.
- Parent requirement - If you are hierarchically structuring your requirements, the parent requirement parameter identifies a broader requirement for every sub-requirement. This way, you can foster relationships among various requirements and ensure proper hierarchy maintenance.
- Priority - The priority parameter assigns priorities to various requirements and enables a better understanding of urgency or relative importance among stakeholders. As a result, it strengthens the decision-making process, offering help with allocating resources and determining the order of implementation of requirements.
- Status - This parameter is responsible for tracking the progress of all requirements as the project lifecycle continues. It helps stakeholders determine the stage of a requirement. In other words, they can easily know whether a requirement is in the proposal stage, has been approved, is being worked on, has been completed, or is subject to future iterations.
- Test Case ID - To verify requirements implementation, all requirements should be associated with one or more test cases. This parameter offers traceability between each requirement and associated testing efforts. As a result, team members can ensure adequate testing and validation of all requirements and whether the system adheres to specific criteria.
- Test result - This is responsible for recording the outcome of test cases that have been executed for a requirement. Test result parameter lets teams know whether they can validate the requirements successfully. It also offers information on issues encountered or if any requirement-related outstanding defects remain.
- Comments or remarks - The comments or remarks section leaves room for additional clarification, information, or discussions associated with specific requirements. It offers a safe space to capture notable remarks like clarifications, change requests, or decision-specific explanations while gathering requirements.
What Are the Types of Requirements Traceability Matrix?
The three types of requirements traceability matrix are forward traceability, backward traceability, and bi-directional traceability.
Forward Traceability
A forward Traceability Matrix checks whether a project is progressing in the right direction. It maps each requirement to its test cases, so you can see whether the requirement is being tested.
Backward Traceability
Also known as reverse traceability, backward traceability ensures product development stays on track, with no unspecified extra functionality that could compromise the project's scope.
It verifies teams are not expanding scope by adding design elements, code, or tests the requirements don't specify, mapping test cases back to their requirements.
Bi-Directional Traceability
Bi-directional traceability ensures that the test cases cover each requirement. It also analyzes how a change impacts requirements. To simplify it, bi-directional traceability ensures the tracing of all test cases to requirements and whether all specified requirements have valid and accurate test cases. The mapping goes both ways.
How Do You Create a Requirements Traceability Matrix Template?
Create an RTM template in three steps: define the goal of the matrix, gather the artifacts such as requirements and test cases, and create the template columns.
Build the template before the full RTM. That involves gathering input documents like a business requirements document and a functional specifications document, and optionally a technical design document.
An RTM template is usually the shell of your Requirements Traceability Matrix. It determines what to trace and why, along with collecting the required documents.
- Define the goal - The first step in creating an RTM template involves defining your goal. Figure out what you are trying to accomplish and deliver with RTM. An example objective includes: creating a Traceability Matrix to prove all compliance requirements for a product are met. When you define the goal before you start the process, you'll be able to gather accurate information for your RTM.
- Gather artifacts - Depending on your objectives, you must define what artifacts you will include. A Traceability Matrix ought to have requirements, tests, test results, and issues. After defining your artifacts, gather them. Every requirement in the list has to have a unique ID which shouldn't change in case of reordering requirements.
This step will also involve tracking your test cases and outcomes and finding test statuses if testing is done or in progress. In case of test failure, you'll have to gather detected issues.
- Create the template - Add a separate column for all your artifacts and start adding them. For a basic Traceability Matrix template, your columns will be requirements, tests, test results, and issues. You can add more as per need.
How Do You Create a Requirements Traceability Matrix in Excel?
Create an RTM in Excel by copying requirements from the requirements document, adding the matching test cases and their results, checking for issues, and updating the matrix consistently.
An RTM is a spreadsheet or table that shows whether all the requirements have their respective test cases. This ensures that during testing, the requirement is fully covered. The process will be a lot smoother if you already have artifact details.
- Copy requirements from the requirements document - Open the document and copy-paste the requirement ID into the template's first column. Depending on the number of requirements, this can be a quick or a lengthy process.
- Copy the test cases - Open your test case documents and copy-paste the test case IDs into the second column of the Excel sheet. You should keep the test cases in the same row as the corresponding requirements they're associated with.
- Copy test results and check for issues - Copy run results and issues from your tracking spreadsheet into the matrix, in the same row as the matching requirements and test cases. Color cells to mark pass or fail.
- Consistently update the Traceability Matrix - The RTM changes as requirements change, so reflect additions or removals while keeping requirement IDs stable. Real-time updates to test cases, test designs, and requirements prevent misalignment.
Here is an example of a Requirements Traceability Matrix you can copy and adapt for a login feature:
| Req ID | Requirement Description | Test Case ID | Status | Defect ID |
|---|---|---|---|---|
| REQ-01 | User can log in with a valid email and password | TC-01, TC-02 | Pass | - |
| REQ-02 | Invalid credentials show an error message | TC-03 | Fail | BUG-114 |
| REQ-03 | Account locks after five failed attempts | TC-04, TC-05 | In Progress | - |
| REQ-04 | Password reset email is sent within 60 seconds | TC-06 | Not Run | - |
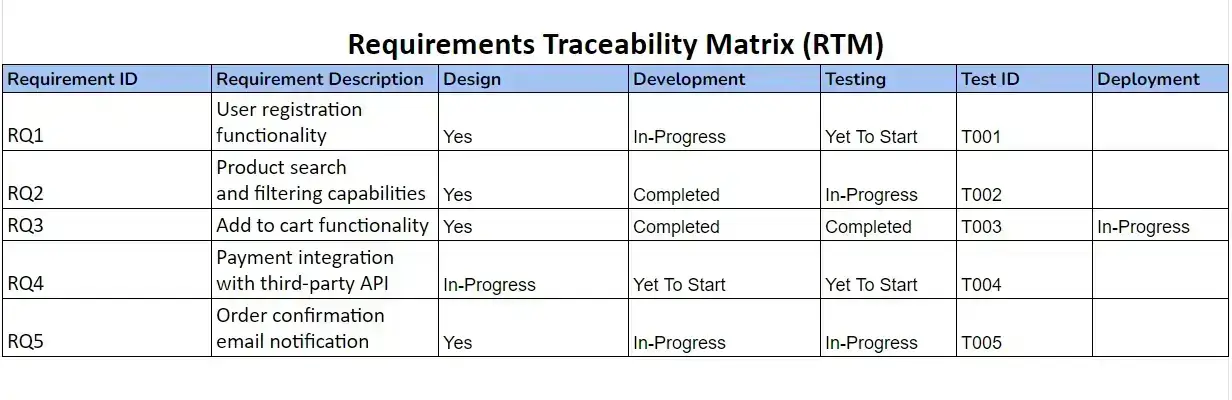
What Is the Difference Between a Covered Requirement and a Proven One?
A requirement is covered when at least one test is linked to it. It is proven when a linked test actually ran against the current build and passed on the assertion for that requirement. Most RTMs only track coverage. A test can be linked and still never have run, or have run on an older version of the requirement.
The difference matters most when tests are written fast, for example by an AI coding agent. A linked test tells you someone intended to check the requirement. It does not tell you the check happened, or that it checked the right thing.
| Requirement | Linked test | Covered? | Last run | Proven? |
|---|---|---|---|---|
| REQ-01 User can sign in with email and password | TC-01 | Yes | Passed on build 412 | Yes |
| REQ-02 Account locks after 5 failed attempts | TC-02 | Yes | Never run | No |
| REQ-03 Locked user sees "Account locked" | TC-03 | Yes | Passed on build 388; requirement edited since | No (stale) |
| REQ-04 Password reset link expires after 24 hours | None | No | Not run | No |
Illustrative example.
To make a spreadsheet RTM show proof as well as coverage, add these columns:
- Last run result and build - the result of the most recent run and the build it ran against, rather than a bare test status.
- Requirement version - the version of the requirement the test was written against, so an edit to the requirement makes the row stale.
- Evidence link - a screenshot, log or run report a reviewer can open.
How Do You Generate a Requirements Traceability Matrix From Test Runs?
You generate an RTM from test runs by tagging every assertion with the ID of the requirement it checks, then reading those tags back from the results of a real run. The matrix then comes out of CI instead of being a document someone updates by hand, and it stays current because it is rebuilt every time the tests run.
The tagging can be as simple as a naming convention in your test framework, or built in. Kane CLI, the terminal testing agent from TestMu AI, builds it into its spec-driven testing flow: kane-cli design tests writes one test per scenario, and each step of a designed _test.md file is an H2 heading. An assert step's heading names, after a @verifies tag, the acceptance criteria that step proves, and the link is recorded when the test is written.
Every run seals an evidence pack, a single .evidence file. When the project has a .context/ requirement store, the pack also carries a coverage record, coverage/usecases.yaml, that lists each acceptance criterion with the test that covers it, its execution result (passed, failed, blocked or not run) and whether it is still fresh (Kane CLI coverage docs). Diff that file between the packs of two full-suite runs to see how a release changed proven coverage. Packs from --remote runs on the cloud grid carry no coverage record.
The cover commands read the matrix back:
kane-cli coverreports coverage for the whole project: the percentage proven and, for each use case, how many criteria passed and whether its source document has changed since. Add--from <pack>to read a single run's coverage from its evidence pack.kane-cli cover gapsadds the design view: how many criteria have a test, and what is still to design or to run.kane-cli cover gaps <uc-id>lists every acceptance criterion of one use case with its state. It works on a local.context/store; in a folder linked to a shared project it is refused, so usekane-cli coverthere.
Run them in the project folder that holds the .context/ store:
# run every *_test.md under the current folder
kane-cli testrun run --headless --agent

# coverage for the whole project, as JSON for a script
kane-cli cover --json > coverage.json

# one use case, criterion by criterion
kane-cli cover gaps <uc-id>
On a 29-criterion coupon feature, using Kane CLI 0.10.2, the last command prints one row per acceptance criterion (rows trimmed here):
$ kane-cli cover gaps uc-1
UC-1 "Manage a cart coupon discount": 62%, partial
  AC-1   The cart page provides a coupon text field and an Apply button.                proven
  ...
  AC-8   Coupon discounts round to the nearest cent with halves rounded up.             not designed
  ...
  AC-18  Submitting BOGUS with no active coupon shows Code not recognised.              not run
  ...
next
  design     kane-cli design tests --use-case uc-1
  first run  kane-cli testrun run   (10 criteria not run)
AC-1 is proven. AC-18 has a test that has not run, so it is covered but not proven. AC-8 has no test at all. In the full run from TestMu AI's Spec Kit walkthrough, 28 of 29 criteria have a test and 18 are proven, so a matrix that only tracked links would overstate this feature by 10 criteria.
To turn that into a matrix, read kane-cli cover --json. Its perAc object has one entry per acceptance criterion, with the state (such as proven, not_run or not_designed), the use case in uc and, for a criterion a run has settled, the deciding_run. That run's evidence pack is .testmuai/evidence/<deciding_run>.evidence. Kane CLI already needs Node.js, so a short script can write the CSV:
// rtm.mjs: one CSV row per acceptance criterion
import { readFileSync, writeFileSync } from "node:fs";

const { perAc } = JSON.parse(readFileSync("coverage.json", "utf8"));
const rows = Object.entries(perAc).map(([id, ac]) =>
  [id, ac.uc, ac.state, ac.deciding_run ?? ""].join(",")
);

const header = "criterion,use_case,state,deciding_run";
writeFileSync("rtm.csv", [header, ...rows].join("\n") + "\n");
The docs do not list these JSON keys, so pin your Kane CLI version and recheck them after an upgrade. For the tests behind each criterion, read coverage/usecases.yaml from the pack. A pack is an ordinary zip file, so unzip -p <pack> coverage/usecases.yaml prints it.
The sample RTM CSV holds all 29 criteria from that coupon run, joined with each requirement's text, its test files from the @verifies tags, and the run and evidence pack that decided it.
Check how the commands behave before you block a release on them:
kane-cli coverandkane-cli cover gapsreport coverage and do not fail a build. Both exit 0 on the coupon feature with 11 of 29 criteria unproven.- Every acceptance criterion cites its source document, and the store keeps each version of that document as a snapshot identified by a hash of its content. When the document changes, everything extracted from the old snapshot reads stale until it is checked again against the new version, which is what
kane-cli maintain reconciledoes (context graph docs). A criterion that passed before the change still counts as proven, so the coverage figure does not drop. The use case is flagged instead:staleis true underperUcinkane-cli cover --json, even whilestale_acsinkane-cli cover gaps --jsonreads 0.
A release check has to read both the proven count and the stale flag. This script fails the job on either, and it exits 1 on the coupon feature, with 11 criteria unproven and uc-1 stale:
// release-check.mjs: fail the job on unproven criteria or a changed requirement
import { readFileSync } from "node:fs";

const { criteria, perUc = [] } = JSON.parse(readFileSync("coverage.json", "utf8"));
const unproven = criteria.total - (criteria.proven ?? 0);
const stale = perUc.filter((uc) => uc.stale).map((uc) => uc.id);

console.log("unproven:", unproven, "stale use cases:", stale.join(" ") || "none");
if (criteria.total === 0 || unproven > 0 || stale.length > 0) process.exit(1);
Prefer a manual matrix? Build one in the free requirements traceability matrix generator, which flags requirements with no tests (GAP) and tests mapped to nothing (ORPHAN), and exports CSV. For team-wide traceability across manual and automated runs, use TestMu AI Test Manager.
What Is a Compliance Matrix?
A compliance matrix is a traceability matrix that maps the regulations, standards, and policies a product must meet to the features and tasks that satisfy them.
If your core aim is to prove compliance, use a specific Traceability Matrix meant for this purpose, known as a compliance matrix. However, there are several complications associated with compliance regulations.
You need to track requirements in a compliance matrix from the said regulations to make it easier to comprehend development and testing. For instance, if your next audit is coming up, you can take some pressure off your shoulders once you create a compliance matrix. This specifically applies if you work in an industry with heavily regulated compliance standards.
Start by listing specifications, requirements, criteria, or standards you need to meet. They can include customer expectations, internal policies, industry standards, legal regulations, and so on. List the requirements on one axis and tasks, features, and components on another. Determine what level of compliance each component holds by reviewing all requirements through audits, tests, or inspections.
Once you are done, allocate a compliance status to each cell, document, supporting information, and associated evidence, including certificates, inspection records, test reports, and other useful documentation. At the same time, don't forget to review non-compliance or partial compliance and address them using the required corrective measures.
Monitor the matrix as new requirements come up and as a project progresses, along with communicating and reporting to stakeholders, team members, customers, project managers, or regulatory authorities. This makes everyone aware and induces transparency around the compliance status of requirements. Creating a Traceability Matrix is advisable as the development continues to make document updates easier. These updates include issue resolutions and other kinds of changes.
What Is a Risk Matrix?
A risk matrix maps probability and severity, letting you calculate risk scores and assess how serious a risk is. It also gives visibility into and management of risk before it grows.
Awareness of a risk makes it easier to avoid by setting a requirement, and a Requirements Traceability Matrix helps you mitigate it more efficiently.
Here is how you can use a risk matrix:
- Identifying the risks - Identify and list potential risks an activity, process, or project might bring. It can be anything with the potential of having a negative impact on one or more objectives, such as reputational damage, operational disruptions, safety hazards, or financial loss.
- Defining risk criteria - A typical risk matrix includes two dimensions, impact and probability. Probability is a representation of how likely a risk event is to occur. Impact represents the consequence or severity of the risk event.
- Create a dual-axis risk matrix - Construct a matrix where rows and columns represent probability and impact, respectively. There should be a range of categories or values for impact and probability in the matrix. They can vary based on risk assessment requirements and complexity.
- Risk assessment - Assign a rating for probability and impact. After evaluating all identified risks, you can carry out these assessments with the help of historical data, experience, expert opinions, etc., and determine the rating for all risks by locating the intersection of probability and impact ratings.
- Risk prioritization - Once you complete the analysis of risk ratings, prioritize risks that require immediate attention as more critical. Cells with a lower rating indicate less severity and a low probability of occurrence.
- Monitoring, communication, and reporting - Monitor risks and keep updating the matrix with new information and share relevant risk matrix findings with stakeholders. Make detailed reports that contain all the necessary information.
Sometimes, mitigating a risk might not be feasible. You either need to eliminate risk or just accept it completely. So, for uncovering potential risks, you should do an FMEA, that is, failure modes and effects analysis, and use the risk matrix to decide what action to take about the said risk.

RTM vs RACI Matrix: What Is the Difference?
A Requirements Traceability Matrix and a RACI matrix are both project artifacts that answer different questions and are easy to confuse. An RTM traces what gets built and tested, linking each requirement to its test cases, results, and defects.
A RACI matrix traces who does the work, mapping each task to who is Responsible, Accountable, Consulted, and Informed. Many projects use both: an RTM for coverage, a RACI for ownership.
| Attribute | RTM (Requirements Traceability Matrix) | RACI Matrix |
|---|---|---|
| Purpose | Trace requirements to tests and defects | Assign roles and responsibilities for tasks |
| Tracks | Requirements, test cases, status, defects | People: Responsible, Accountable, Consulted, Informed |
| Answers | Is every requirement tested and covered? | Who owns and signs off on each task? |
| Typically owned by | QA, test leads, business analysts | Project or program managers |
| Output | Coverage and gap evidence for audits | Clear accountability and communication |
How Does Traceability Work in Agile Teams?
In Agile teams, traceability links user stories and their acceptance criteria to tests, code changes and defects, sprint by sprint. Instead of one large matrix signed off at the end, links are created as stories are written and kept current by tooling. The goal is the same: show which requirements are tested and which are not.
Practical rules that keep it light:
- Give every acceptance criterion an ID inside the story (AC-1, AC-2). Writing it in EARS notation gives it a stated trigger and an expected system response.
- Reference that criterion ID in the test as well as the story ID.
- Let CI produce the matrix from test results each sprint.
- Review only the gaps (criteria with no test, tests with no criterion, and links left stale after a story changes).
Match the depth of tracing to risk. Stories that move money or handle personal data need the full chain from story to commit, test and defect, while a cosmetic change can stop at its story link. On a new product, start with the most critical features of the first release and extend the matrix as later sprints add features. Save a version of the matrix at each major release so coverage can be compared from one release to the next.
When several teams build one product, link stories across teams as well. If the mobile team's sign-in screen depends on a backend team's authentication API story, that link shows the dependency at sprint planning instead of at integration. Tie each backlog level to the one above it (epic, feature, story, acceptance criterion), so a test result on a criterion can be traced up to its epic.
How Do You Create a Traceability Matrix in Jira?
You create a traceability matrix in Jira by linking each requirement to the work items that fulfill and test it. Atlassian publishes a requirements traceability matrix template built this way, using Jira's issue linking to connect each requirement to its tasks, user stories, or test cases, with custom dashboards for requirement status.
A Jira admin can add a custom link type with its own outward and inward descriptions (Jira work item linking docs).
Name one for testing, with a pair such as "tests" and "is tested by", so a test link is easy to tell apart from a general relation.
If your test cases live in TestMu AI's Test Manager, open the Issues tab of a test case, click Link requirement, and enter the Jira issue key. The issue is then listed under Requirements (link Jira issues with Test Manager). Requirements and defects are in slow rollout, so until they are enabled for your organization, linked issues appear in a single list.
What Are the Limitations and Challenges of a Requirements Traceability Matrix?
The main RTM limitations are manual maintenance overhead, stale data in static spreadsheets, many-to-many complexity, and no single source of truth.
An RTM is only as useful as it is current, and keeping it current is where most teams struggle:
- Manual maintenance overhead - Every new requirement, test case, or defect has to be reflected by hand, so the matrix competes with actual testing work for time.
- Stale data in static spreadsheets - An RTM kept in Excel drifts out of date the moment a requirement changes and no one updates the sheet, so it stops reflecting reality.
- Many-to-many complexity - On large projects one requirement maps to many tests and one test covers many requirements, and that web is hard to maintain and read in a flat spreadsheet.
- No single source of truth - When requirements live in one tool, tests in another, and the RTM in a third, the three fall out of sync.
These limits are why teams move traceability into a test management platform. TestMu AI Test Management tool links requirements to test cases, runs, and defects automatically, so the matrix updates itself as tests execute and stays audit-ready without manual upkeep. See the Test Manager documentation to set it up.
Keeping each automated test on its original manual case is covered in how to convert manual test cases to automated tests.

Note: Stop maintaining traceability by hand. TestMu AI Test Manager links every requirement to its tests, runs, and defects in one workspace and keeps the matrix current automatically. To try it, start free.
What Are the Best Practices for a Requirements Traceability Matrix?
RTM best practices include bi-directional traceability, linking stakeholders to requirements, keeping the matrix updated, formal reviews, unique identifiers, and clear priorities and dependencies.
- Extra focus on bi-directional traceability - Combining forward and backward traceability lowers risk and improves transparency, letting you trace lower-level requirements to their source and back, so every requirement is fully addressed.
- Connecting contributors and stakeholders to relevant requirements - Link people to the requirements they own so the right quality assurance staff, developers, architects, analysts, and testers join decisions at the right time.
- Keeping the RTM updated at all times - An RTM that lags behind the requirements gives false confidence, so update it in the same workflow that changes a requirement, test case, or result.
- Conducting formal reviews - Formal reviews against industry regulations and internal controls keep interdependent requirements compliant. Show how each requirement links to test plans and passed tests, ideally with a requirements management tool that generates review reports.
- Have a clear and consistent definition of the RTM structure - Having a clear and consistent definition of the RTM structure that's simple to follow and understand results in consistent terminology, formats, column headings, etc., across the matrix. This enhances clarity and eliminates any possible confusion among stakeholders and team members.
- Maintain uniqueness in identifiers - One of the best traceability practices is to assign unique identifiers to entities like test cases, design elements, and requirements that the RTM includes. It helps maintain clarity and traceability links and facilitates straightforward referencing and cross-referencing of various entities.
- Establishing clear traceability relationships - Clarity in defining and maintaining traceability relationships between test cases, design, artifacts, and requirements is a good practice. Make sure you use appropriate references, linking mechanisms, and symbols to represent all the relationships accurately.
- Practice requirement prioritization - Add priorities to the requirements based on project constraints, customer needs, or business value. It helps guide the sequencing of efforts and development, resource allocation, and good decision-making.
- Don't overlook dependencies and assumptions - One of the most common traceability mistakes team members make is that they overlook dependencies and assumptions. It's important to document assumptions during the design or requirement-gathering stages and identify dependencies. Always document these dependencies, whether they are between requirements or other project components. This practice enables stakeholders to understand the potential impact and context of any changes.
How Is AI Changing Requirements Traceability?
AI is changing requirements traceability by suggesting links between requirements and test cases, flagging requirements with no test, and generating draft test cases from requirement text.
When a requirement changes, AI-assisted impact analysis can list the linked tests to rerun, which keeps regression testing focused instead of rerunning everything.
Suggested links still need human review, because a model can match on shared words rather than real intent, and regulated teams must keep an auditable record of who approved each link. Our roundup of AI test case generation tools compares tools that generate cases from requirements.
AI coding agents write tests quickly, which makes "a test is linked" weaker evidence than before. In a TestMu AI experiment on six small functions with one seeded bug each, 22 of 60 AI-written unit test suites that could see the buggy code still passed on it, against 0 of 60 suites written only from each function's documented contract. Traceability now needs to record what was proven, not only what was linked.
Conclusion
Start with a simple spreadsheet RTM that maps each requirement ID to its test cases and results, then move it into a test management tool as the project grows.
Add the last run result, the requirement version, and an evidence link to each row, so the matrix shows proof as well as coverage. Once your tests run in CI, generate the matrix from those runs and fail the release check on unproven or stale requirements.
Tracking tests across tools and teams? TestMu AI's Test Manager keeps test cases, runs and results in one place.
Author
Harshit Paul
Blogs: 97


Harshit Paul is Director of Product Marketing at TestMu AI, with over 8 years of experience in product and growth marketing for developer and QA tools, leading the Agentic AI in Quality Engineering space. He has authored 80+ technical articles for TestMu AI on software testing and automation, and hosted webinars on Selenium, automation testing, browser compatibility, DevOps, and continuous testing. He has led go-to-market and technical marketing initiatives across software testing products, contributing to SEO, content strategy, and developer marketing. He began his career as a certified Salesforce developer at Wipro Technologies, where he worked for 2 years before moving into marketing. Harshit holds a degree in computer programming from Vivekananda Institute of Professional Studies.
Reviewer
Abhishek Mishra
Reviewer
Abhishek Mishra is a Technical Product Manager at TestMu AI, where he owns Test Manager, the test management product. He has over 8 years of experience in product management and market analysis. His expertise spans across AI-native software testing, product strategy, and analytics. Previously, Abhishek served as the Product Lead at IndiaClan and co-founded Gartley618 Technologies, where he led innovative projects in quantitative trading and blockchain. He holds a B.Tech degree.


Requirements Traceability Matrix FAQs
Did you find this page helpful?
More Related Learning Hubs











TestMu AI forEnterprise
Get access to solutions built on Enterprise
grade security, privacy, & compliance
- Advanced access controls
- Advanced data retention rules
- Advanced Local Testing
- Premium Support options
- Early access to beta features
- Private Slack Channel
- Unlimited Manual Accessibility DevTools Tests